Quick answer
Crypto billing platform security should be evaluated by tracing how money and authority move: what a customer wallet approves, what the smart contract can execute, whether the provider can access merchant funds, how payment events reach your application, and who can change withdrawal or contract settings. Before launch, require verifiable evidence for each control, assign an internal owner, and test failure paths rather than accepting a security page as proof.
The crypto billing platform security decision starts with control of funds
Choose a platform only after you can prove who can move customer and merchant funds under normal operation, compromise, and recovery. “Non-custodial” is useful only when the architecture prevents the provider from holding or unilaterally redirecting your money.
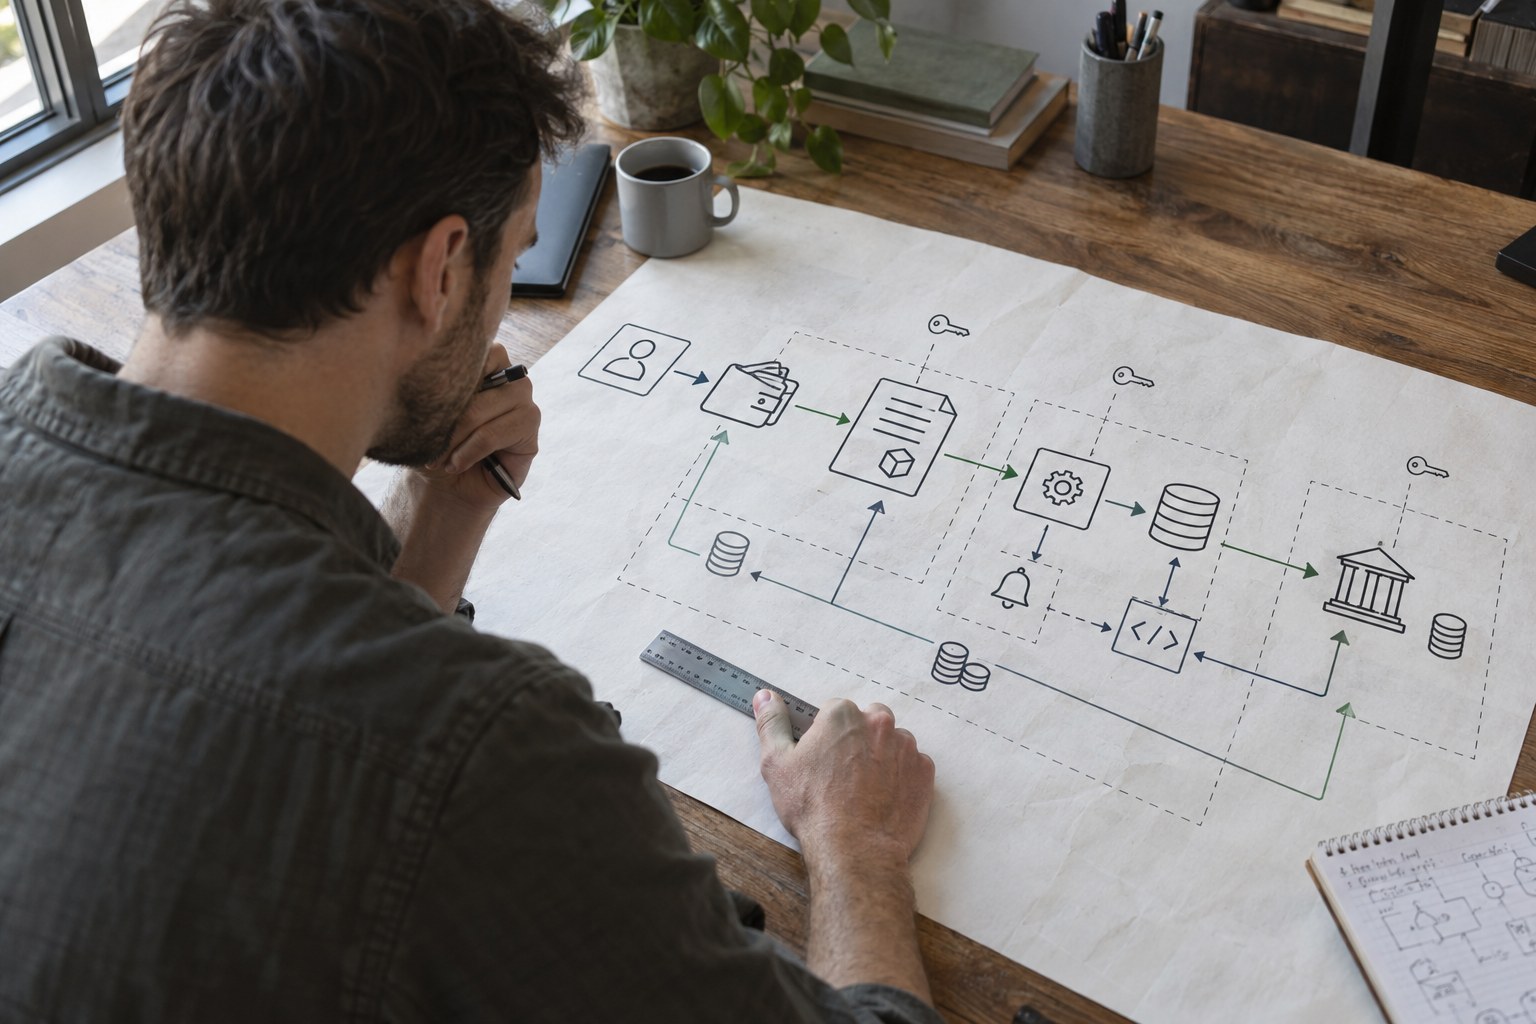
Start with four assets: customer token allowances, merchant settlement addresses, billing records, and privileged credentials. Then map every actor able to affect them: the customer wallet, billing contract, platform backend, your application, administrators, and treasury signers. A provider may never possess your private key yet still expose you through an upgrade key, editable destination address, forged webhook, or excessive token allowance. The practical test is therefore authority, not vocabulary: identify each action that can move value or grant service and the independent control that stops abuse.
| Decision question | Acceptable evidence | Reject or escalate when |
|---|---|---|
| Can the provider take custody? | A documented fund flow showing settlement directly to the merchant wallet | Funds enter a provider-controlled omnibus wallet |
| Can billing authority exceed the plan? | Approval scope, collection rules, cancellation path, and deployed contract behavior are inspectable | The customer signs an unlimited or unclear permission without an operational need |
| Can one administrator redirect value? | Role separation, strong authorization, change records, and treasury approval controls | One routine account can alter destinations or privileged contract settings |
| Can a fake event grant service? | Authenticated, replay-resistant, idempotent webhook processing | A successful HTTP request alone activates an account |
How should wallet permissions and smart contracts be reviewed?
Customer authorization should be understandable, bounded to the intended billing relationship, and revocable. The contract should enforce those boundaries even if a user interface or backend is compromised; a polished confirmation screen is not a security boundary.
Review the exact approval and collection sequence on every supported network and token. The customer should see the asset, relevant spender, and economic meaning before signing, while your support team should know how revocation and cancellation work. Inspect privileged contract functions separately: pause, upgrade, fee, destination, role assignment, and recovery powers deserve more scrutiny than routine collection. Ask whether privileged calls use separated roles or multi-party authorization, whether changes are delayed or monitored, and what happens to existing subscriptions after an upgrade. This is where a documented crypto billing platform architecture becomes a security control rather than an integration diagram.
- Record deployed contract addresses and verified source or equivalent review material for each production network.
- Test maximum charge, billing interval, cancellation, expired authorization, insufficient balance, and unauthorized caller behavior.
- Identify every privileged role, its key storage, approval policy, emergency power, and replacement process.
- Confirm that merchant private keys and seed phrases never enter platform forms, support channels, application logs, or deployment secrets.
- Require a pause and customer-communication plan that does not depend on the same credential suspected of compromise.
How do you stop forged webhooks and address substitution?
Treat blockchain state as the payment record and webhooks as authenticated notifications about that record. Never grant durable service from an unverified callback, and never let a silently changed address redefine where revenue settles.
A webhook endpoint is public, so authenticate the raw request before parsing or acting on it. Verification should cover the delivered body and freshness data, use constant-time signature comparison, reject stale deliveries, and deduplicate events. Processing must be idempotent because legitimate retries happen. After authentication, validate the expected network, token contract, amount, merchant destination, transaction identifier, and confirmation policy against your own order record. A strong crypto billing integration testing plan includes forged signatures, altered payloads, replays, duplicates, delayed events, chain mismatch, and out-of-order delivery.
| Threat | Required control | Monitor | Owner |
|---|---|---|---|
| Forged payment event | Per-endpoint secret and verified signature | Authentication failures and unusual source patterns | Application security |
| Replay or duplicate | Freshness check plus event-key idempotency | Repeated identifiers and stale timestamps | Backend engineering |
| Address substitution | Allowlisted destination bound to merchant configuration | Destination changes and mismatches | Treasury operations |
| Incorrect chain state | Independent transaction-field validation | Reverted, replaced, or unconfirmed transactions | Payments engineering |
What does a pre-launch threat matrix look like in practice?
The checklist should connect each plausible loss event to provider evidence, your internal control, a detectable signal, and one accountable responder. A control without an owner is usually documentation wearing a hard hat.
Consider a hypothetical SaaS merchant with the explicit assumptions that subscriptions settle directly to one operating wallet and treasury staff sweep funds to a separately controlled reserve wallet. The billing platform should not hold either private key. Engineering owns webhook verification and entitlement logic; security owns secrets and alerting; finance owns settlement reconciliation; designated treasury signers own destination changes and withdrawals. During the launch drill, compromise a test administrator, replay a valid event, submit a payment to the wrong destination, and invoke an unauthorized contract action. Passing means each attempt is blocked or detected before value or service is incorrectly released.
- Wallet exposure: obtain proof that merchant signing material is unnecessary; prohibit seed-phrase entry and scan logs for secret leakage.
- Contract abuse: document privileged functions and deployed addresses; monitor administrative calls; assign containment to security and contract engineering.
- Webhook forgery: verify signatures and freshness before processing; alert on failures; assign recovery to application engineering.
- Address substitution: require independent authorization for destination changes; reconcile every settlement; assign approval to treasury.
- Privileged-access takeover: enforce least privilege and strong authentication; review role and configuration changes; assign account containment to security.
- Treasury loss: separate operating and reserve authority; alert on unexpected transfers; assign investigation and recovery decisions to named signers.
This exercise exposes a common ownership gap: the provider may secure its contract and delivery service, while the merchant still mishandles entitlements, administrator accounts, or treasury keys. Record expected evidence for every drill step, including rejected requests, alerts, transaction details, and the person authorized to declare recovery. Do not accept “the team will notice” as monitoring. If responsibilities span vendors or departments, place the handoff and escalation contact in the runbook. The next action is to run the matrix as an observed launch gate, not a questionnaire completed by procurement alone.
How should you implement and approve the platform?
Approve in stages: architecture evidence first, hostile integration tests second, restricted production exposure third, and operational sign-off last. Compliance, accounting, customer support, and incident response remain merchant responsibilities even when the platform is non-custodial.
Translate the threat matrix into acceptance criteria before connecting a production wallet. Resolve contract addresses, roles, customer approval behavior, settlement destinations, webhook verification, secret rotation, reconciliation, logging, and emergency contacts. Then define crypto payment monitoring around events that require action: privileged contract calls, destination edits, repeated signature failures, abnormal collection results, and reconciliation mismatches. Security should approve technical controls; finance should approve fund flows and treasury ownership; product should approve cancellation and entitlement behavior; legal or compliance advisers should assess the merchant’s own obligations in each market and industry.
- Document the complete authority and fund-flow model, including recovery paths.
- Collect platform evidence and record unresolved assumptions in a crypto billing platform RFP.
- Test contract, wallet, webhook, address, entitlement, and reconciliation failure cases.
- Launch with constrained permissions, separated roles, named responders, and actionable alerts.
- Review production evidence after the first billing cycle and after every material contract, destination, role, or integration change.
A non-custodial design is a poor fit when the business actually needs a provider to convert assets, hold balances, manage treasury decisions, or absorb all regulatory and operational work. It also cannot reverse an on-chain transfer or rescue a compromised merchant key. For teams that do want direct wallet settlement, the final verification is simple: complete one test subscription from approval through collection, entitlement, reconciliation, cancellation, and incident review. Preserve the evidence, obtain named sign-off, and only then expand production access. Security becomes an operating routine, not a procurement adjective.
Apply the checklist to direct wallet subscriptions
Zyrox supports direct wallet payments and subscriptions using USDT, USDC, and Bitcoin. For recurring billing, customers authorize through their wallet, while smart-contract subscriptions automate collection and funds settle directly to the merchant wallet rather than a third-party custodian.
Zyrox charges a 0.5% platform fee. If self-custody, recurring on-chain billing, payment links, webhooks, and API integration match your control model, evaluate the live flow against the checklist above and keep your own compliance, treasury, and incident responsibilities explicit.
Frequently asked questions
What is the most important crypto billing platform security control?
Prove who can move funds or change payment authority. Map customer approvals, contract privileges, settlement addresses, administrator roles, and merchant keys before evaluating secondary controls.
Does non-custodial crypto billing eliminate platform risk?
No. It removes custody-related exposure when funds settle directly to the merchant, but contract flaws, privileged roles, forged events, compromised merchant keys, and integration errors can still cause loss.
Should a crypto billing platform ever request a seed phrase?
No legitimate billing integration needs the merchant’s seed phrase. Signing should remain in the merchant-controlled wallet or approved signing system.
How should recurring wallet permissions be limited?
The customer should understand the token, spender, billing purpose, and cancellation path. The contract must enforce the intended collection rules, while the merchant tests revocation and expired or insufficient authorization.
How should crypto payment webhooks be secured?
Verify an authenticated signature over the original delivery, enforce freshness, reject replays, deduplicate events, process idempotently, and validate transaction fields against the merchant’s own order record.
Who should control the merchant settlement wallet?
The merchant should control its wallet and signing policy. Separate routine operating activity from reserve treasury authority, constrain destination changes, and require independent approval for sensitive transfers.
Is an audited smart contract enough for launch approval?
No. Contract review does not secure webhook handlers, administrator accounts, address changes, entitlement logic, treasury keys, monitoring, or incident response. Those controls require separate evidence and testing.
How often should crypto billing security be reviewed?
Review it before launch, after material changes to contracts, networks, wallet destinations, roles, or integrations, and whenever monitoring or an incident reveals that an assumption no longer holds.
Dmitry Alentev
Builds SaaS platforms for content creators, agencies, and entrepreneurs. Writes about the business mechanics behind creator-economy products and how custom software actually ships.
Reviewed under our Editorial standards.